ISPConfig自動安裝script

設定好 master / slave hostname

cd /root

curl -fsSL \
  https://get.ispconfig.org \
  -o ispconfig-ai.sh

sh /root/ispconfig-ai.sh --help
sh /root/ispconfig-ai.sh \
  --channel=stable \
  --lang=en \
  --interactive \
  --use-php=5.6,7.0,7.1,7.2,7.3,7.4,8.0,8.1,8.2,8.3,8.4,8.5 \
  --no-mail \
  --no-dns \
  --no-local-dns \
  --no-roundcube \
  --no-pma \
  --no-ftp \
  --no-jailkit \
  --no-quota \
  --no-firewall

這份選項的重點:

  • Apache 是預設,不需要另外加 --use-apache。
  • --interactive 必須保留,才能選 expert 並加入 Master。
  • 關閉郵件主機、DNS、FTP、Webmail、phpMyAdmin 等不需要的角色。
  • 本次不安裝 Jailkit、不設定 quota,也不讓安裝器接管 UFW。(howtoforge.com)

另外注意:

--no-mail 仍可能安裝 Postfix 供系統寄信,不表示完全沒有郵件相關套件。(howtoforge.com)

不要加 --no-web! 它會連 Apache 網站服務一起停用,並不是單純取消管理介面。管理介面稍後在互動問題選 n。(howtoforge.com)

PHP 版本方面,這裡的 5.x 目標是 5.6,不是 5.0~5.5;最新的 8.x 支援範圍要看實際安裝器,不能保證它會安裝所有已發行的 8.x。PHP 5.6 與所有 7.x 均已停止官方支援,只建議用於必要的舊站相容用途。(howtoforge.com)

ISPConfig 多 PHP 版本環境下應對 CVE-2026-115560 漏洞:全域修復與服務重啟實戰

在現今複雜的網頁寄存環境中,主機控制面板通常需要同時支援多個不同的 PHP 版本(從舊版的 PHP 5.4、5.6 到現代的 PHP 7.x、8.x),以滿足不同客戶或網站系統的相容性需求。然而,當突發重大安全漏洞(如針對 session.upload_progress 的 CVE-2026-115560 遠端程式碼執行漏洞)降臨孤立或多版本並存的伺服器時,管理員如何在不破壞多 PHP 架構的前提下進行一次性全域快速止血,就成為了一門重要的技術課題。

本文將以實際在 ISPConfig 伺服器上的防護經驗為例,分享如何利用 Shell Script 精準修復多版本 php.ini 並安全重啟服務。

一、 挑戰所在:ISPConfig 多 PHP 架構的配置特點

以採用 Remi 套件庫並透過 ISPConfig 管理多 PHP 版本的 Linux 伺服器為例:

  • 路徑分散:系統中往往同時存在多個獨立的 PHP 運行環境,其設定檔並非集中在單一的 /etc/php/ 目錄,而是散落于 /opt/remi/、/etc/opt/remi/ 或 /etc/ 等自訂路徑中。
  • 版本眾多:從 PHP 5.4 一直到 PHP 8.3 共存,若手動逐一打開每個版本的 php.ini 進行修改,不僅耗時費力,還極容易遺漏高風險版本。

二、 實戰演練:一次性全域修改 php.ini

為了精準切斷 CVE-2026-115560 的漏洞觸發路徑(即關閉 session.upload_progress.enabled 且不影響正常的檔案上傳功能),我們不需要「一刀切」禁止所有上載,而是可以直接在伺服器端執行一段迴圈腳本,自動掃描並更新所有版本的 php.ini。

1. 執行自動掃描與批次修改指令

透過以下 Shell 命令,系統會自動在 /opt/、/etc/ 及 /usr/local/ 中尋找所有的 php.ini 檔案:

  • 若檔案中已存在該參數,則自動將其設定為 0;
  • 若不存在,則在檔案結尾自動追加 session.upload_progress.enabled = 0。

Bash

for ini in $(find /opt/ /etc/ /usr/local/ -type f -name "php.ini" 2>/dev/null); do
    if grep -q "session.upload_progress.enabled" "$ini"; then
        sed -i 's/^[# \t]*session\.upload_progress\.enabled\s*=.*/session.upload_progress.enabled = 0/' "$ini"
    else
        echo "session.upload_progress.enabled = 0" >> "$ini"
    fi
    echo "已更新: $ini"
done

執行後,終端機會清晰列出所有被成功加固的 php.ini 路徑,確保無一遺漏。

三、 批次重啟 PHP-FPM 與網頁伺服器

設定檔修改完成後,必須重啟對應的 PHP-FPM 服務與網頁伺服器(以 Apache / httpd 為例),才能使全域修改正式生效。

1. 迴圈重啟各版本 PHP-FPM 服務

Bash

for s in php54-php-fpm php56-php-fpm php70-php-fpm php72-php-fpm php73-php-fpm php74-php-fpm php81-php-fpm php83-php-fpm; do
    systemctl restart $s 2>/dev/null
    echo "已重啟: $s"
done

2. 重啟網頁伺服器

Bash

systemctl restart httpd

四、 總結與防護建議

透過這套自動化處理方案,系統管理員能在短短數分鐘內完成整台 ISPConfig 多 PHP 版本伺服器的漏洞防護加固:

  1. 精準 surgical 級別防禦:關閉 session.upload_progress.enabled 有效阻斷了 RCE 攻擊途徑。
  2. 業務零中斷:完整保留了網站正常的檔案上傳與互動功能,避免粗暴禁止上傳所帶來的業務癱瘓。
  3. 高效維運:利用 Shell 迴圈完美解決了多版本、分散式路徑的管理難題。

建議各位主機維護團隊在面對新型自動化攻擊浪潮時,優先採用這類結構化、自動化的指令碼來提升應變效率,保障伺服器的絕對安全。

✅ How to Fix ISPConfig Manual SQL Backup Not Working (While Auto Backup Works)

Problem Overview

In ISPConfig 3.3 multi‑server setups, you may encounter the following issue:

  • ✅ Scheduled (Automatic) SQL backups work normally
  • ❌ Manual SQL backup does nothing
  • ❌ No error message appears
  • ❌ No backup folder is created
  • ✅ Some websites may work, others do not

This behavior can be confusing because everything seems healthy — but manual backups simply don’t trigger.

This article explains the root cause and provides the permanent fix.


Why This Happens

ISPConfig handles backups differently:

✅ Automatic Backup

Runs locally on the SQL server via cron and does not rely on datalog synchronization.

❌ Manual Backup

Uses this flow:

  1. The ISPConfig UI writes a task into sys_datalog (on the Master server)
  2. The SQL server reads the datalog entry
  3. server.sh processes the task
  4. Backup runs

If the datalog entry cannot be properly written or transmitted, the manual backup will silently fail.


The Real Cause: max_allowed_packet Too Small

In most cases, the issue is caused by a MariaDB configuration problem:

max_allowed_packet

On Debian 12/13 and many CentOS installs, the default is:

16M

In some cases, even:

1M

That is too small for ISPConfig 3.3 multi‑server environments.

Why?

Because sys_datalog may contain:

  • SSL certificate blobs
  • Large JSON configuration data
  • Backup metadata
  • Website configuration structures

If a datalog record exceeds max_allowed_packet, MariaDB silently rejects the transfer.

Result:

  • Small websites → manual backup works
  • Larger websites → manual backup does nothing
  • Auto backup still works

How to Check Your Current Value

Run on BOTH Master and SQL server:

mysql -u root -p -e "SHOW VARIABLES LIKE 'max_allowed_packet';"

If you see:

16777216  (16M)

or smaller → this is your problem.


✅ The Permanent Fix (Debian 13 / MariaDB 10.11+)

Step 1 — Edit MariaDB Configuration

On Debian 13, edit:

/etc/mysql/mariadb.conf.d/50-server.cnf

Find the [mysqld] section and set:

max_allowed_packet = 256M
wait_timeout = 300
interactive_timeout = 300

Save the file.


Step 2 — Restart MariaDB

systemctl restart mariadb

Verify:

mysql -u root -p -e "SHOW VARIABLES LIKE 'max_allowed_packet';"

You should now see:

268435456

Step 3 — Reset Stuck Datalog Entries

On the Master server:

mysql -u root -p dbispconfig

Run:

UPDATE sys_datalog SET processing = 0;

Then on the SQL server:

/usr/local/ispconfig/server/server.sh

After Fixing

Manual SQL backups should now:

  • ✅ Work for all websites
  • ✅ Create backup folders immediately
  • ✅ No longer silently fail

Why 256M Is Recommended

For ISPConfig multi‑server setups:

SettingRecommended Value
max_allowed_packet256M
wait_timeout300
interactive_timeout300

256M ensures large SSL or configuration payloads do not break datalog synchronization.


Important Notes

✅ You must update BOTH Master and SQL servers
✅ Restart MariaDB after changes
✅ Clear stuck datalog entries

If you only update one server, the problem may persist.


Final Thoughts

If you see:

  • Manual SQL backup does nothing
  • No error in UI
  • Auto backup works
  • Some sites succeed, others fail

The issue is almost certainly MariaDB’s max_allowed_packet.

Increasing it to 256M resolves the problem permanently in almost all ISPConfig 3.3 multi‑server environments.

Debian 13 + ISPConfig 3.3 + Slave Installation and config

1️⃣ Install Debian 13

最小安裝完成後:

apt update
apt upgrade -y

2️⃣ Enable Root Login

nano /etc/ssh/sshd_config

加入或修改:

PermitRootLogin yes

重新啟動 SSH:

systemctl restart ssh

3️⃣ Set Static IP

nano /etc/network/interfaces

加入:

auto ens18
iface ens18 inet static
    address 10.0.0.x
    netmask 255.255.255.0
    gateway 10.0.0.1
    dns-nameservers 8.8.8.8 8.8.4.4
    up ip route add 10.y.0.0/24 via 10.0.0.z
    down ip route del 10.y.0.0/24 via 10.0.0.z

確認無拼字錯誤。


4️⃣ Reboot

reboot

5️⃣ Set DNS

nano /etc/resolv.conf

內容:

nameserver 8.8.8.8
nameserver 8.8.4.4

6️⃣ Test Network

ping google.com

若可解析並 ping 通,表示 DNS 正常。


7️⃣ Edit Hosts

nano /etc/hosts

加入:

10.0.0.w    master.ispconfig.domain

(確認 IP 與實際 master 相符)


8️⃣ Install ISPConfig

cd /tmp
wget -O - https://get.ispconfig.org | sh -s -- --interactive

9️⃣ Installation Mode

Installation mode (standard,expert) [standard]: expert

🔟 Join Multiserver Setup

Shall this server join an existing ISPConfig multiserver setup (y,n) [n]: y

11️⃣ MySQL Master Information

MySQL master server hostname []:
master.ispconfig.domain
MySQL master server root password []:

⚠ 必須:

  • 知道 master 的 MySQL root password
  • 並且 master MySQL 必須允許 slave IP 連線

在 master 上確認:

GRANT ALL PRIVILEGES ON *.* TO 'root'@'10.0.0.x' IDENTIFIED BY 'password' WITH GRANT OPTION;
FLUSH PRIVILEGES;

12️⃣ Keep MySQL Root Password

安裝過程中會顯示:

  • MySQL root password

請保存。


13️⃣ Remove Install Logs

rm /root/ispconfig-install-log/setup-*

避免密碼留在系統中。


14️⃣ Set Default PHP Version

update-alternatives --config php

選擇:

php 7.4

否則 slave cronjob 會無法與 master 正常連線。

確認:

php -v

✅ Installation Complete

登入:

https://slave.ispconfig.domain:8080

使用 master 帳號登入。


WordPress Installation

  1. ISPConfig → Sites → Add Website
  2. 建立 Database
  3. 上傳 WordPress
  4. 設定 wp-config.php
  5. 完成安裝

如果你需要,我可以:

  • 幫你排成「正式教學文件格式」
  • 或整理成「公司內部 SOP 文件版」
  • 或轉成 PDF 版教學稿

告訴我你要哪種格式。

acme.sh renew

source : https://www.howtoforge.com/getting-started-with-acmesh-lets-encrypt-client/#renew-the-lets-encrypt-ssl-certs

Install Let’s encrypt SSL cert

Apache example:

acme.sh --install-cert \
--domain example.com \
--cert-file /path/to/cert/cert.pem \
--key-file /path/to/keyfile/key.pem \
--fullchain-file /path/to/fullchain/fullchain.pem \
--reloadcmd "sudo systemctl reload apache2.service"

Renew the Let’s Encrypt SSL certs

acme.sh --renew -d example.com --force

ISPConfig 3 API, List all domain_id

Attention: Before using this script, you MUST KNOW how to use ISPConfig API. If you are first time to learning ISPConfig API, Please go to see First time test ISPConfig API learning how to config, how to run it and how to debug with https.

File name: sites_web_domain_id_get_all.php
<?php

require 'soap_config.php';

$context = stream_context_create([
    'ssl' => [
        // set some SSL/TLS specific options
        'verify_peer' => false,
        'verify_peer_name' => false,
        'allow_self_signed' => true
    ]
]);

$client = new SoapClient(null, array('location' => $soap_location,
                'uri'      => $soap_uri,
                'trace' => 1,
                'exceptions' => 1,
                'stream_context' => $context));

try {
        if($session_id = $client->login($username, $password)) {
                echo 'Logged successfull. Session ID:'.$session_id.'<br />';
        }


        $domain_record = $client->sites_web_domain_get($session_id, []);
        $domain_ids = array_column($domain_record, 'domain_id');


        print_r($domain_ids);

        if($client->logout($session_id)) {
                echo 'Logged out.<br />';
        }


} catch (SoapFault $e) {
        echo $client->__getLastResponse();
        die('SOAP Error: '.$e->getMessage());
}

?>

First time test ISPConfig API

  • After Install ISPConfig , the application would not saved any API Example or Document. So, we need to find out the example scripts at the source file and copy them to /usr/local/ispconfig.
cd /tmp 
wget -O ispconfig.tar.gz https://www.ispconfig.org/downloads/ISPConfig-3-stable.tar.gz
tar xfz ispconfig.tar.gz
cd ispconfig3_install/
cp -R remoting_client/ /usr/local/ispconfig/
cd /usr/local/ispconfig/remoting_client
  • All API Document and example file was copied to /usr/local/ispconfig/remoting_client
  • ISPConfig add Remote Users
ISPConfig Web UI > system > Remote User > Add new user

Entry username & password, And click what do you want function. In first test, please click all Functions. Please remember username & password for modify API config file .

save
  • Modify API config file
cd /usr/local/ispconfig/remoting_client/examples/
nano soap_config.php
<?php

$username = 'admin';
$password = 'admin1234';

/*
$soap_location = 'http://localhost:8080/ispconfig3_3.0.5/interface/web/remote/index.php';
$soap_uri = 'http://localhost:8080/ispconfig3_3.0.5/interface/web/remote/';
*/


$soap_location = 'https://192.168.1.100:8080/remote/index.php';
$soap_uri = 'https://192.168.1.100:8080/remote/';


?>

Change to

<?php

$username = 'username';
$password = 'password';

/*
$soap_location = 'http://localhost:8080/ispconfig3_3.0.5/interface/web/remote/index.php';
$soap_uri = 'http://localhost:8080/ispconfig3_3.0.5/interface/web/remote/';
*/


$soap_location = 'https://localhost:8080/remote/index.php';
$soap_uri = 'https://localhost:8080/remote/';


?>
  • Test First API
php system_config_get.php

If every was ok, you will see the follow message.

Logged successfull. Session ID:qd0758c7265f2498285bef4e2f7ba4a3a25f8c7e3<br />Array
(
    [company_name] => Innonext
    [custom_login_text] =>
    [custom_login_link] =>
    [dashboard_atom_url_admin] => https://www.ispconfig.org/atom
    [dashboard_atom_url_reseller] => https://www.ispconfig.org/atom
    [dashboard_atom_url_client] => https://www.ispconfig.org/atom
    [tab_change_discard] => n
    [tab_change_warning] => n
    [use_loadindicator] => y
    [use_combobox] => y
    [show_support_messages] => y
    [maintenance_mode] => n
    [maintenance_mode_exclude_ips] =>
    [admin_dashlets_left] =>
    [admin_dashlets_right] =>
    [reseller_dashlets_left] =>
    [reseller_dashlets_right] =>
    [client_dashlets_left] =>
    [client_dashlets_right] =>
    [customer_no_template] => C[CUSTOMER_NO]
    [customer_no_start] => 1
    [customer_no_counter] => 5
    [session_timeout] => 0
    [session_allow_endless] => n
    [min_password_length] => 8
    [min_password_strength] => 3
)
  • Normally, It was Done! BUG

But some API have some BUG and not work. This is because the normally working API was disabled ‘ssl verify peer’ when using https connect. So, we need add ‘disabled ssl verify peer’ in not work API.

Test sites_web_domain_get.php, you will get a error message ‘SOAP Error: Could not connect to host‘

php sites_web_domain_get.php
SOAP Error: Could not connect to host[root@system]#

Fix method, Edit sites_web_domain_get.php

<?php

require 'soap_config.php';

{add something here}

$client = new SoapClient(null, array('location' => $soap_location,
                'uri'      => $soap_uri,
                'trace' => 1,
                'exceptions' => 1{add something here}));


try {
        if($session_id = $client->login($username, $password)) {
                echo 'Logged successfull. Session ID:'.$session_id.'<br />';
        }

        //* Set the function parameters.
        $subdomain_id = 10;

        $subdomain_record = $client->sites_web_subdomain_get($session_id, $subdomain_id);

        print_r($subdomain_record);

        if($client->logout($session_id)) {
                echo 'Logged out.<br />';
        }


} catch (SoapFault $e) {
        echo $client->__getLastResponse();
        die('SOAP Error: '.$e->getMessage());
}

?>

Change to

<?php

require 'soap_config.php';

$context = stream_context_create([
    'ssl' => [
        // set some SSL/TLS specific options
        'verify_peer' => false,
        'verify_peer_name' => false,
        'allow_self_signed' => true
    ]
]);

$client = new SoapClient(null, array('location' => $soap_location,
                'uri'      => $soap_uri,
                'trace' => 1,
                'exceptions' => 1,
                'stream_context' => $context));

try {
        if($session_id = $client->login($username, $password)) {
                echo 'Logged successfull. Session ID:'.$session_id.'<br />';
        }

        //* Set the function parameters.
        $subdomain_id = 10;

        $subdomain_record = $client->sites_web_subdomain_get($session_id, $subdomain_id);

        print_r($subdomain_record);

        if($client->logout($session_id)) {
                echo 'Logged out.<br />';
        }


} catch (SoapFault $e) {
        echo $client->__getLastResponse();
        die('SOAP Error: '.$e->getMessage());
}

?>

Test sites_web_domain_get.php again

php sites_web_domain_get.php
Logged successfull. Session ID:u3712304db1b527b09cbe8582f141f0614331d551<br />Logged out.<br />[root@system]#
  • Everything Done.
  • You may not research other API in /usr/local/ispconfig/remoting_client/examples.
  • About API Document, you may direct file download to you desktop computer.

https://www.ispconfig.org/downloads/ISPConfig-3-stable.tar.gz

Extract ISPConfig-3-stable.tar.gz in your PC.

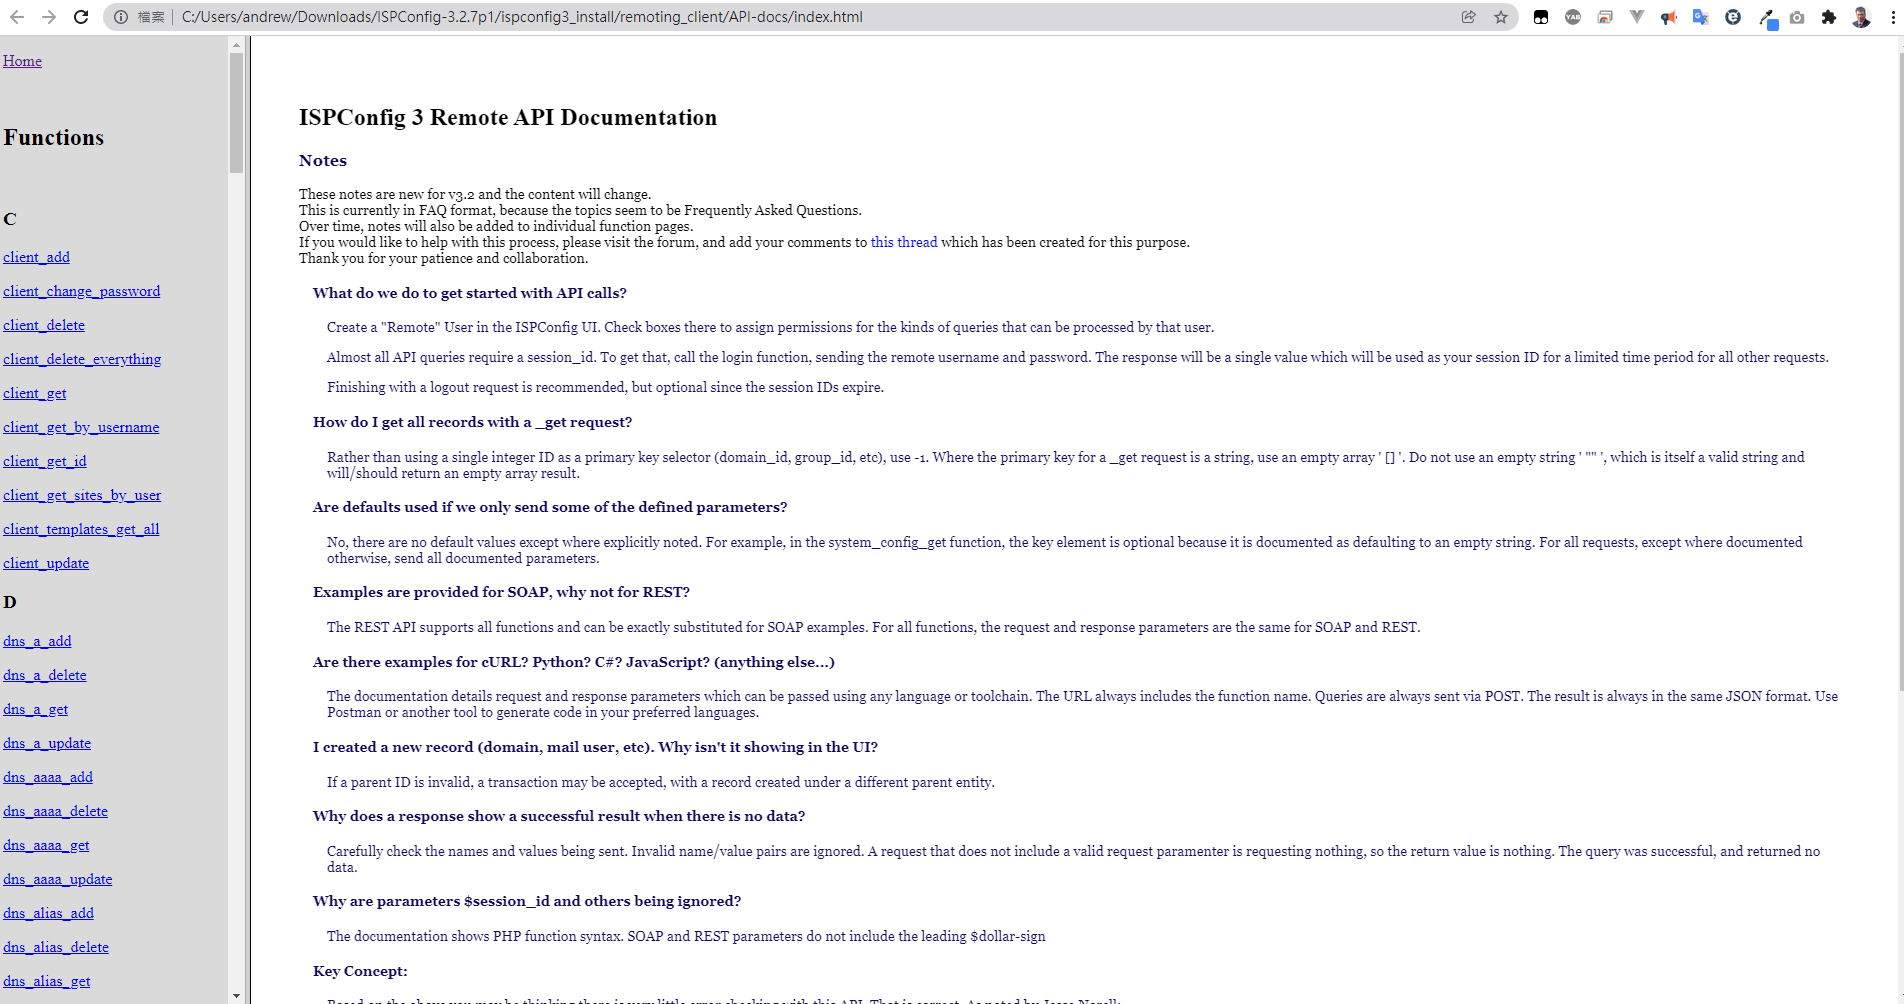
You may find a file in extracted folder and run it, Ispconfig3_install\remoting_client\API-docs\index.html

Fixed MySQL replication slave got Last_SQL_Errno: 1062

If you don’t want REDO the complete procedure, a good fix would be to use

STOP SLAVE;    
SET GLOBAL sql_slave_skip_counter=1;
START SLAVE;

If there are too many such errors, a good idea would be to automate it using a bash script.

Reference : Ut xD(2017), https://serverfault.com/questions/336888/what-causes-the-mysql-error-1062-duplicate-entry-when-starting-slave, Last visit at Jan 2022
Manuel SQL backup for ISPConfig by command line

Version 3.1.x

The following command will start cron job backup in advance.

command: cron_debug.php

php /usr/local/ispconfig/server/cron_debug.php --cronjob=500-backup.inc.php

Version 3.2.x

command: backup-now.php

Usage:
php backup-now.php --id=<4> [--type=]
Options:
--id id of the website to backup.
--type backup type: all, web or mysql. Default is all.
php /usr/local/ispconfig/server/backup-now.php --id=1 --type=mysql